New
-
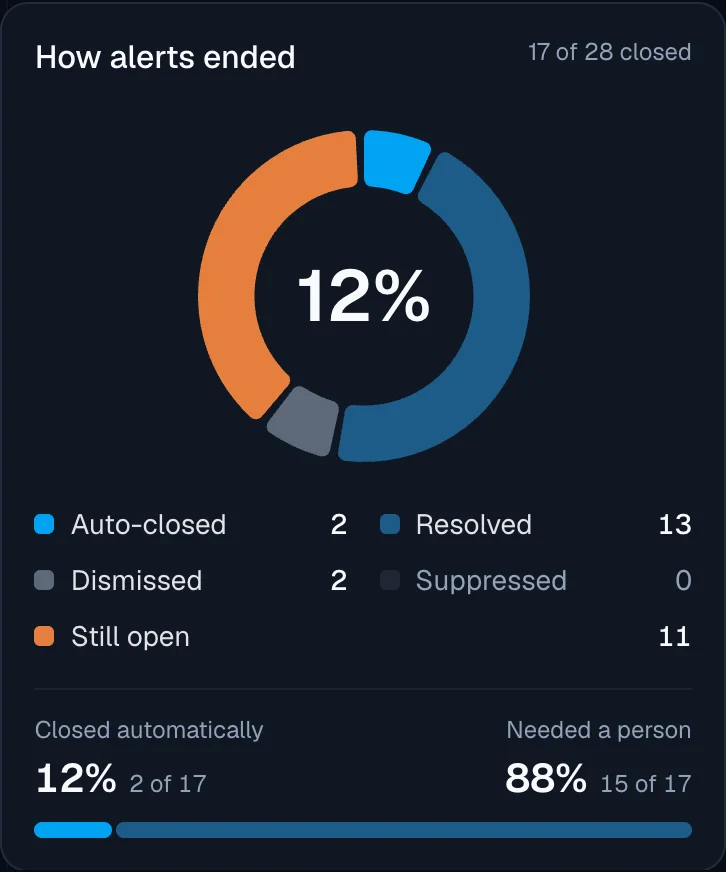
See how many alerts closed on their own. The How alerts ended card on the dashboard now shows, inside the ring, the share of closed alerts that Jutsu closed by itself. Under the legend, Closed automatically and Needed a person each show a percentage and a count of the closed alerts. Hover the figure to see how many closed alerts it counts.
Improved
- Alerts are raised sooner. New events are ready for detection every 5 seconds instead of every 15. Rules for a source that sends rarely, such as code scans, no longer wait up to 5 minutes before they look at its new events, and an organization's rules now run several at a time instead of one after another.
- Refused attack attempts close on their own. When an attack is only refused calls from a caller that was not signed in, such as a burst of permission denied errors, and none of them succeeded, Jutsu now closes the alert at triage as an attempt with no success. Before, the alert stayed escalated for about three hours while Jutsu waited for late records. Jutsu still checks those records when they arrive: if a call succeeded, or the check cannot finish, the alert reopens and is escalated. While the attempt is closed, more of the same calls do not raise new alerts.
- Mean time to detect counts from when an alert could be raised. When an earlier alert on the same rule was holding back repeat alerts and a new alert is raised as soon as that hold ends, the MTTD figure now counts from the end of the hold instead of from the first event. Before, the hold made detection look slower than it was.
- AWS Cloud checks list each problem once. Under Compliance, Cloud checks, a check that fails in several AWS regions is now one row, for example "AWS Config is not recording in 2 regions", with its regions listed. Open the row to see each region. A new region filter narrows the list, and the page's link keeps it.
- Fewer AWS findings for regions you do not use. In an AWS region where Jutsu finds no resources and GuardDuty is on, four checks no longer count as problems: AWS Config recording, EBS default encryption, default security group rules, and flow logs on the default VPC. Flow logs on a default VPC with nothing attached no longer count in any region. GuardDuty turned off is still reported in every region. If a resource appears or GuardDuty is turned off, the next daily scan reports the check again, and a finding's history says why it was set aside.
- Clearer names on the dashboard and Connections. On the dashboard, External sources is now Attacks by IP, with the address first and its country beside it, and ATT&CK coverage and activity is now MITRE ATT&CK Coverage. On Connections, the Applications group is now Monitors.
Fixed
- The People page in the Sandbox shows its list again instead of an error.