New
-
Jutsu now closes the alerts it can settle by itself, and each closed alert says why:
- An attack attempt where nothing got through closes as Resolved. If a later check finds that it did succeed, the alert reopens and notifies you.
- A vulnerability alert from Jutsu's dependency scan or Dependabot closes once its finding is in Code Security, which tracks it until it is fixed or dismissed.
- An AI review closes alerts it judges are not a real security issue, inside limits Jutsu enforces. It never closes a critical alert, and never one about account takeover, secrets, cleared logs, admin grants, defense evasion, execution, impact or data exfiltration.
Nothing a person set or answered on an alert is changed.
-
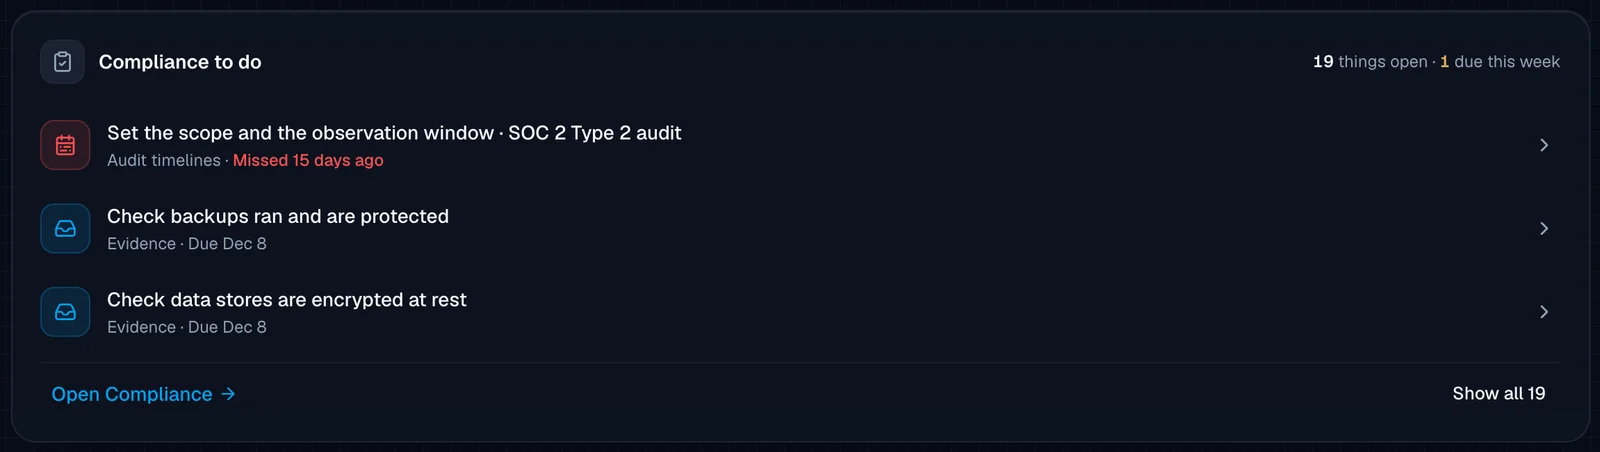
Action Center: "Compliance to do" now sits under Needs you. It shows the next three compliance tasks (policy approvals, evidence and documents due, vendor and risk reviews, audit findings and audit timelines), how many are open and how many are due this week. "Show all" opens the full list in place.
-
Fix steps on a cloud finding and on its risk now use the real resource name, such as the bucket or the user, instead of a placeholder. The finding page links the resource and adds a button such as "Open the bucket in AWS" (Google Cloud and Azure resources get the same), and the risk page puts that link on the first fix step.
Improved
- Action Center: risks from one failing check on one connection now fold into a single row under Needs you, named the way the Risks list names the group, for example "Public access is allowed on 10 storage buckets". Open takes you to that group on the Risks page, and the arrow expands the row to show each risk.
- Risks from Google Workspace, GitHub and AWS account checks now name the account (an email, a GitHub @login or an AWS user name) instead of an internal ID, and open with what is wrong with that account. Google Workspace 2-step verification risks link to the account's page in Google Admin.
- A link to a risk, alert or incident now opens in the organization that holds it, even when you are working in another one.
- The connection type chart at the top of the Risks page can be collapsed.
- The AI agents page in Organization settings is now called MCP, and so is the screen where you approve an MCP client.
- Jutsu AI knows about recent console changes, including monitors, the Azure, Supabase and Render connections, and alerts that close themselves.
Fixed
- Employee portal: the link in a policy email now opens the portal for that email's organization, for people who belong to more than one. Someone without a seat in the organization is told so, instead of "Something went wrong on our side."
Docs
- Weekly release notes: a longer roundup of each week's releases, at /release-notes.