New
-
Three AWS CloudTrail rules: Assume-role trust policy widened, VPC Flow Logs disabled, and Secrets Manager secret accessed. The Secrets Manager rule alerts on secrets read by a person rather than an application, and it is off by default; turn it on under Rules.
-
The Windows collector installer now turns on the Windows audit settings that Jutsu's Windows rules read: process creation with command lines, scheduled tasks, account and group changes, audit policy changes and logons. It prints every setting it changes, and
-SkipAuditPolicyleaves the host's audit policy alone. Re-run the installer on hosts that already have the collector to apply the settings. -
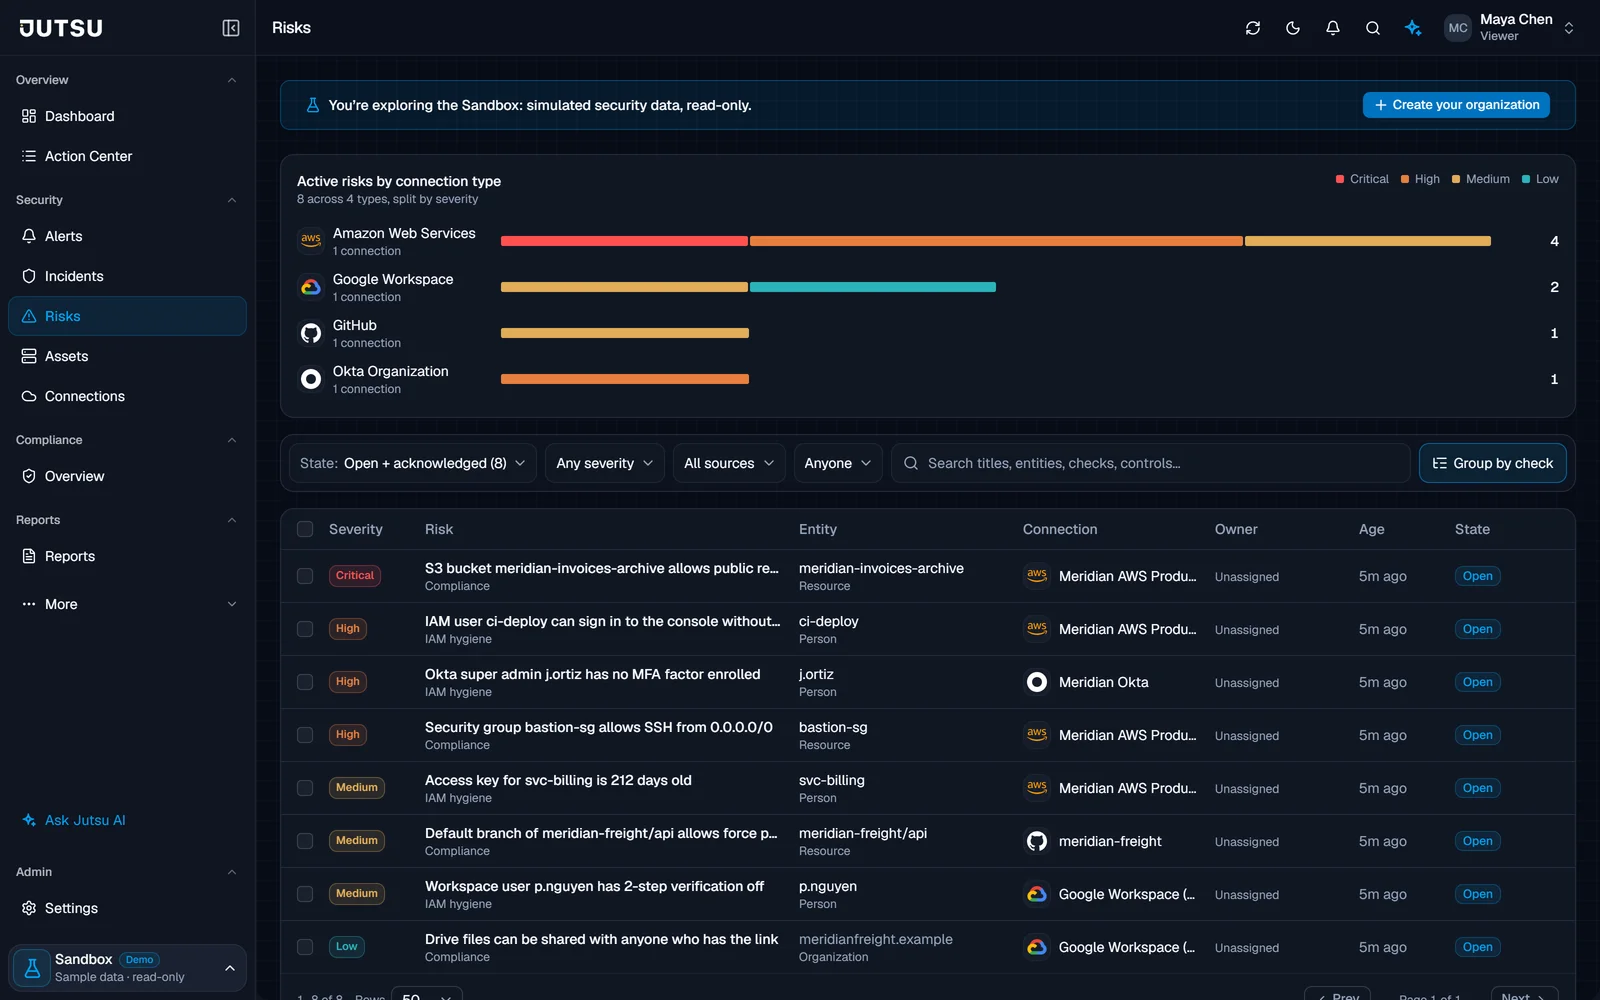
Risks: filter the list by connection type. A chart of risks by connection type and severity replaces the tiles at the top of the Risks page.
Improved
-
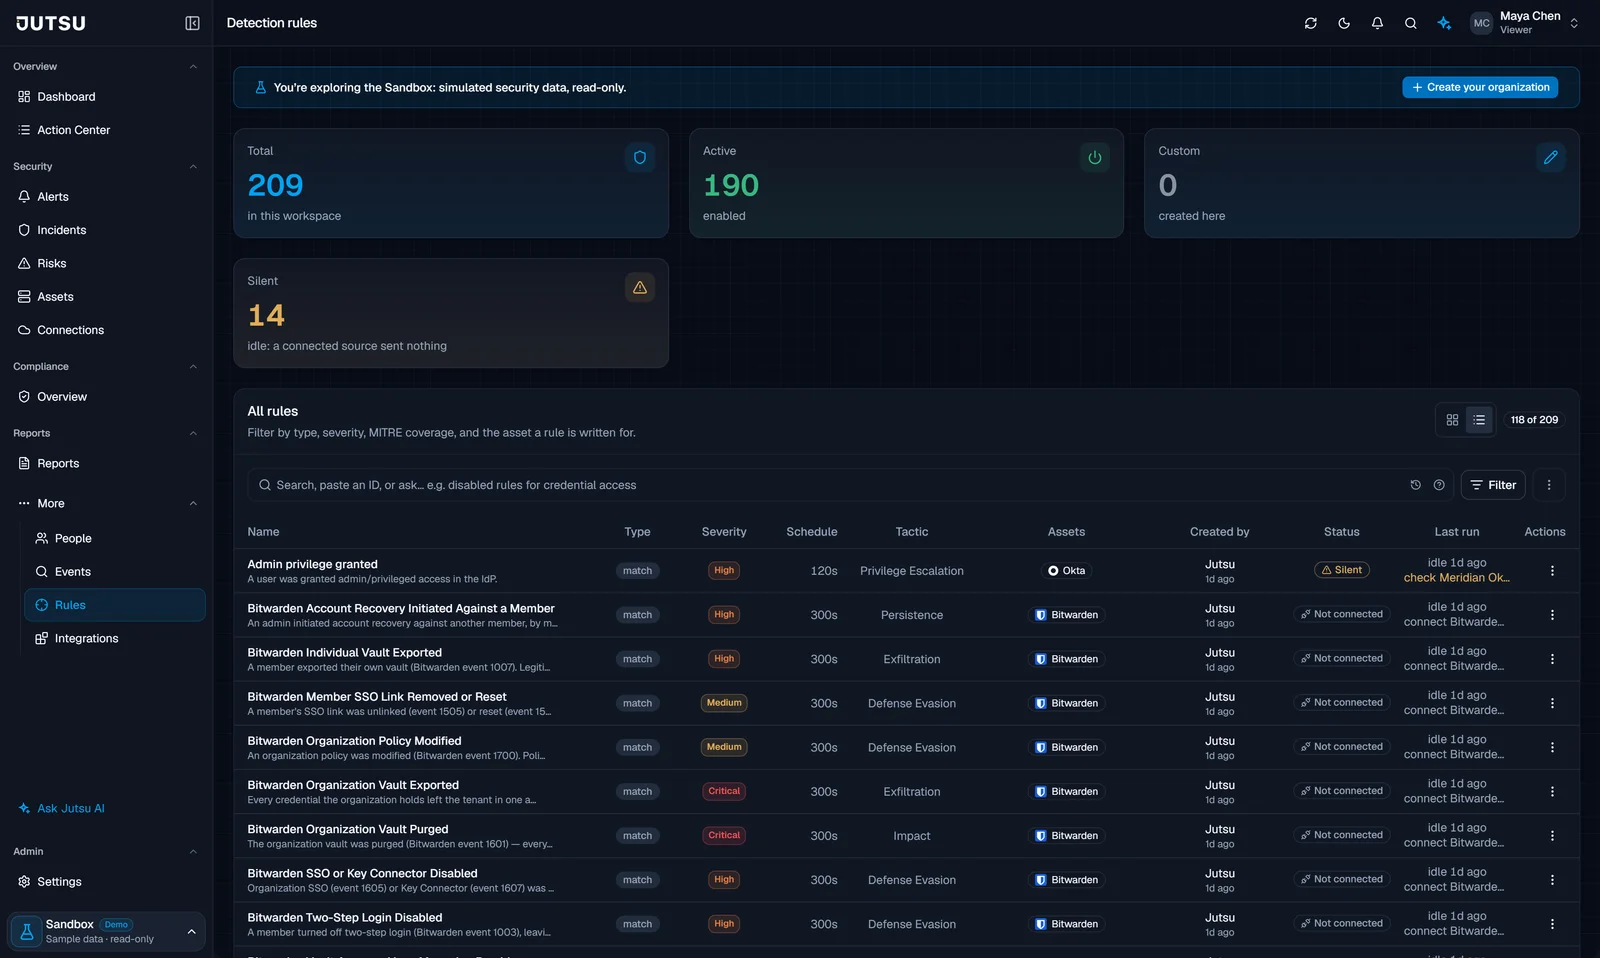
Rules: an idle rule now says why it is idle. "Silent" means a source you connected sent nothing in the last 24 hours, with a link to that connection. "Not connected" means you have not connected that source; those rules are folded away by default, and the State filter can show them.
-
Pipeline Health and the dashboard's ingestion card now judge a source by when its events arrive, and show how many of them were stored for rules. A source whose events all fall below its Minimum severity no longer shows as down.
-
AWS connections: when GuardDuty or Security Hub is not turned on in the AWS account, the connection page says so in a neutral note with links to turn them on, instead of a "Needs attention" warning.
Fixed
- Detection rules that could not fire at the default Medium severity setting now see their events:
- AWS CloudTrail: Security group opened to the world, S3 bucket made public, GuardDuty disabled, AWS Config recorder stopped, KMS key disabled or scheduled for deletion, EBS snapshot shared externally, IAM login profile created, IAM policy modification, and Account password policy weakened.
- Command-line rules on Windows, Linux and macOS: Suspicious PowerShell execution, LOLBin remote download, Credential dumping (LSASS), Endpoint security tooling tampering, Shadow copy / backup deletion and Linux reverse shell. Sysmon process events now feed them too.
- Sign-in rules (Failed logins followed by success, Impossible travel, Anomalous login behavior) now see successful sign-ins from Okta, Microsoft 365, Cloudflare Access, 1Password, Bitwarden and LastPass.
- Cloudflare: log delivery changes, rate-limit rule changes, Access application, group and identity provider changes, Worker and route deployments, bulk DNS changes, and Access granted after repeated denials.
- Vercel: actions from the audit log drain are graded the same as the activity feed, and a secret file served to a probe is detected.
- Okta MFA push denials, Bitwarden secrets read from the CLI, Docker container log rules, and web attack signatures in URLs from Cloudflare, Railway, Supabase and webhook sources.
- GCP: "privileged role granted", "firewall rule opened to the internet" and "long-lived credential created" now match Google's real audit log records.
- "S3 bucket made public" now also catches a bucket policy that allows everyone and Block Public Access being removed.
- "Security group opened to the world" no longer matches private address ranges such as 10.0.0.0/8.
- Routine commands no longer look like attacks:
sc query windefend,rsync -e sshand PowerShell's-Encodingargument. - "RDP brute force" now explains that hosts with Network Level Authentication log failed RDP logons as a different logon type, which "Windows account brute force" covers.
- Rules: Viewers, and anyone exploring the Sandbox, no longer see "Forbidden" over a rules table that loaded fine.
- Jutsu AI: a complete answer is no longer marked "The response stopped before it finished.", and a chat started near the end of a sign-in session no longer loses its data lookups partway through.