An AI security operations platform, built for startups
Jutsu watches your AWS, Google Workspace, GitHub and laptops 24/7. AI agents check every alert, and fixes run only when your team or your policy says so.
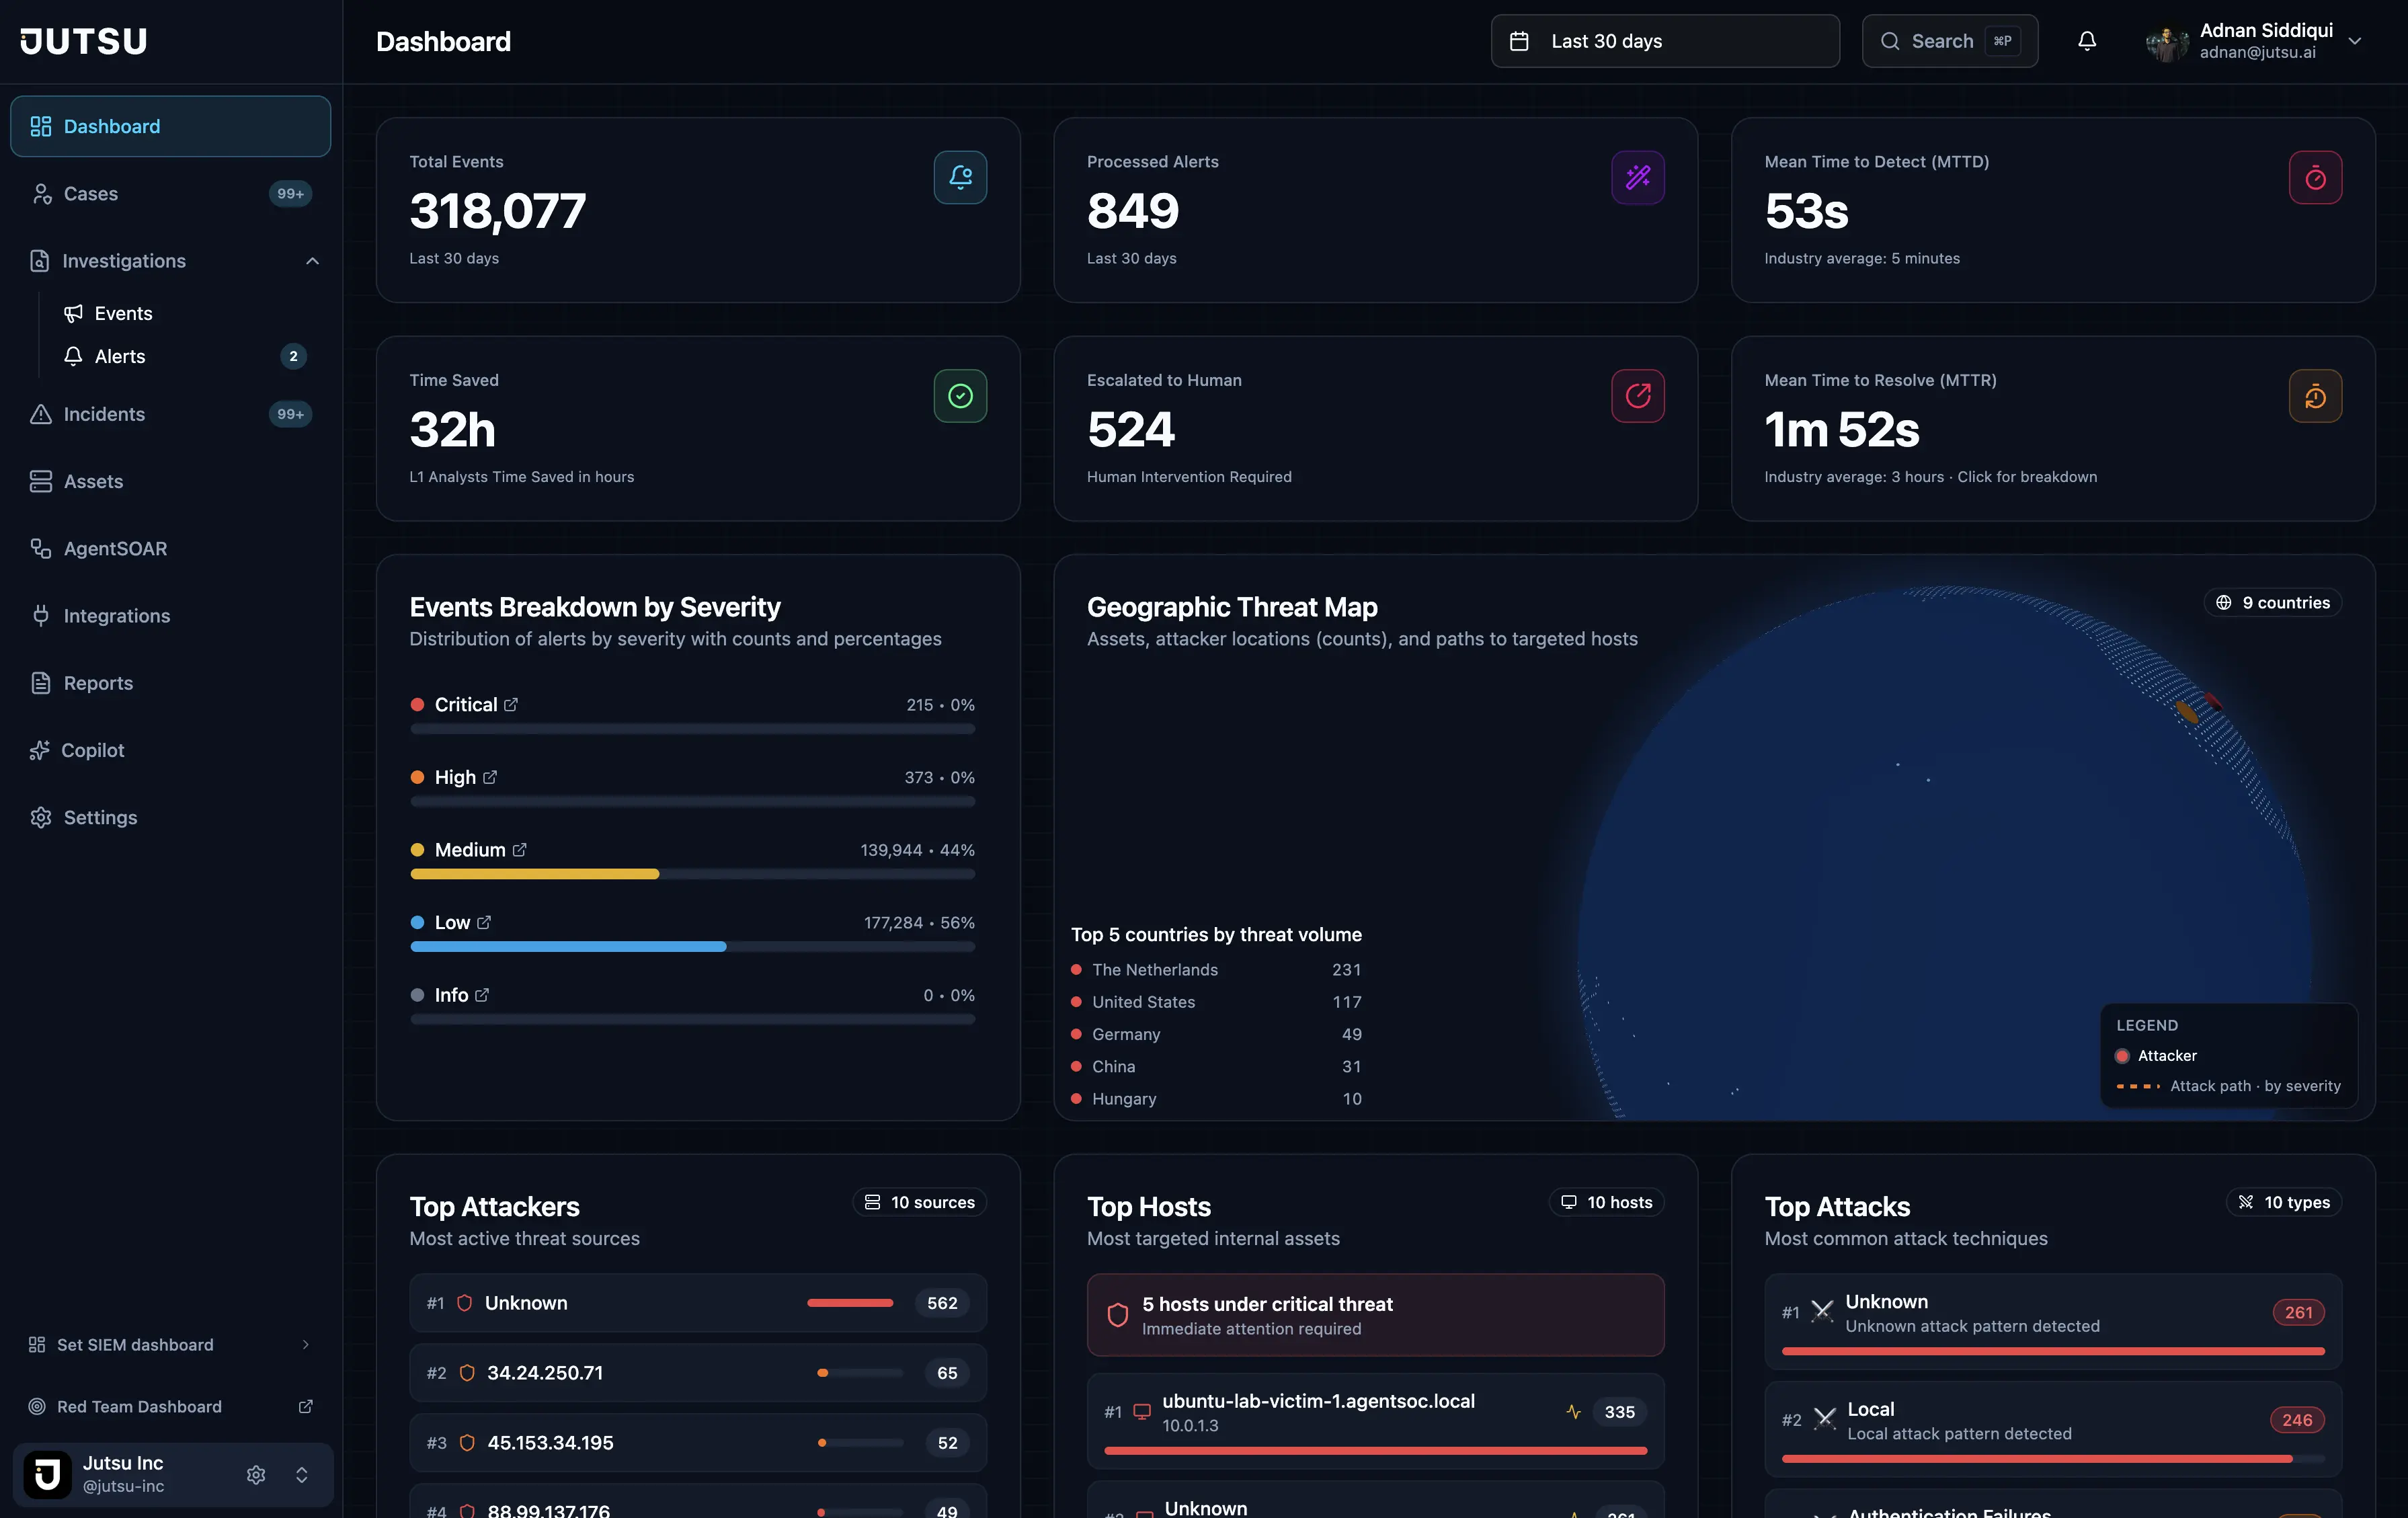
- Every alert in one placeCloud, sign-in, code, and laptop alerts land in one list instead of five consoles.
- AI takes the first lookAI agents look up every alert, rate how serious it is, and group related ones.
- You make the callWhen the agents aren't sure, they ask a person. Every action is logged and can be undone.
- Awake at 3 a.m.Alerts are checked around the clock, including nights and weekends.
Up and running in three steps
Connect what you run on
AWS, Google Cloud, Azure, Google Workspace, GitHub, Vercel, Supabase, Cloudflare, Railway, and your laptops and servers. Most take about 10 minutes.
AI agents check every alert
They look up IPs, files, and domains in threat intelligence, rate how serious each alert is, and group related alerts into one incident.
Fix it, or ask you
When an alert is real, Jutsu proposes the fix, such as blocking an IP or disabling a user. When it isn't sure, it asks you. Every step is logged.
Everything in Jutsu
AI alert triage
Each alert gets a category, severity, risk score, and verdict before anyone on your team opens it.
Incident correlation
Related alerts become one incident, so an attacker moving from one machine to the next reads as one story.
Incident & case management
Follow each incident and its investigation from the first alert to closed, in one place.
Geographic threat map
A 3D globe of attacker origins, event volumes, and attack paths to your assets.
Automated SOAR response
Block an IP, isolate a laptop, or disable a user through the built-in AgentSOAR engine or Shuffle, and undo it if needed.
Security Copilot
A natural-language Copilot that queries your alerts, incidents, cases, and enrichment data.
What teams use Jutsu for
Cybersecurity for startups
Watch AWS, Google Workspace, GitHub, and your team's laptops without building a security team.
Security monitoring for startups
What to log and alert on first in AWS, Google Workspace, GitHub, Vercel, and Supabase, watched 24/7.
SOC 2 for startups
Get SOC 2 ready with policy drafts, evidence tasks, daily checks, and security monitoring that runs.
SOC 2 continuous monitoring
Daily control checks plus 24/7 security monitoring, with the records CC7.2 to CC7.4 ask for.
SIEM for startups
Jutsu collects your logs and AI checks every alert, so a startup gets a SIEM and someone to read it.
Autonomous SOC
AI agents run the SOC workflow end to end. Analysts keep the critical decisions.
AI alert triage
Every alert classified, enriched, and correlated before an analyst opens it.
AgentSOAR
The SOAR built into Jutsu: AI decides the response, AgentSOAR runs it, with revert.
Wazuh AI SOC
AI triage, correlation, and response for Wazuh alerts. Keep Wazuh, add the SOC.
AI SOC platform comparison
Jutsu against Torq, Cortex XSIAM, and Charlotte AI: what we document, and what to ask.
Explore the rest of the platform
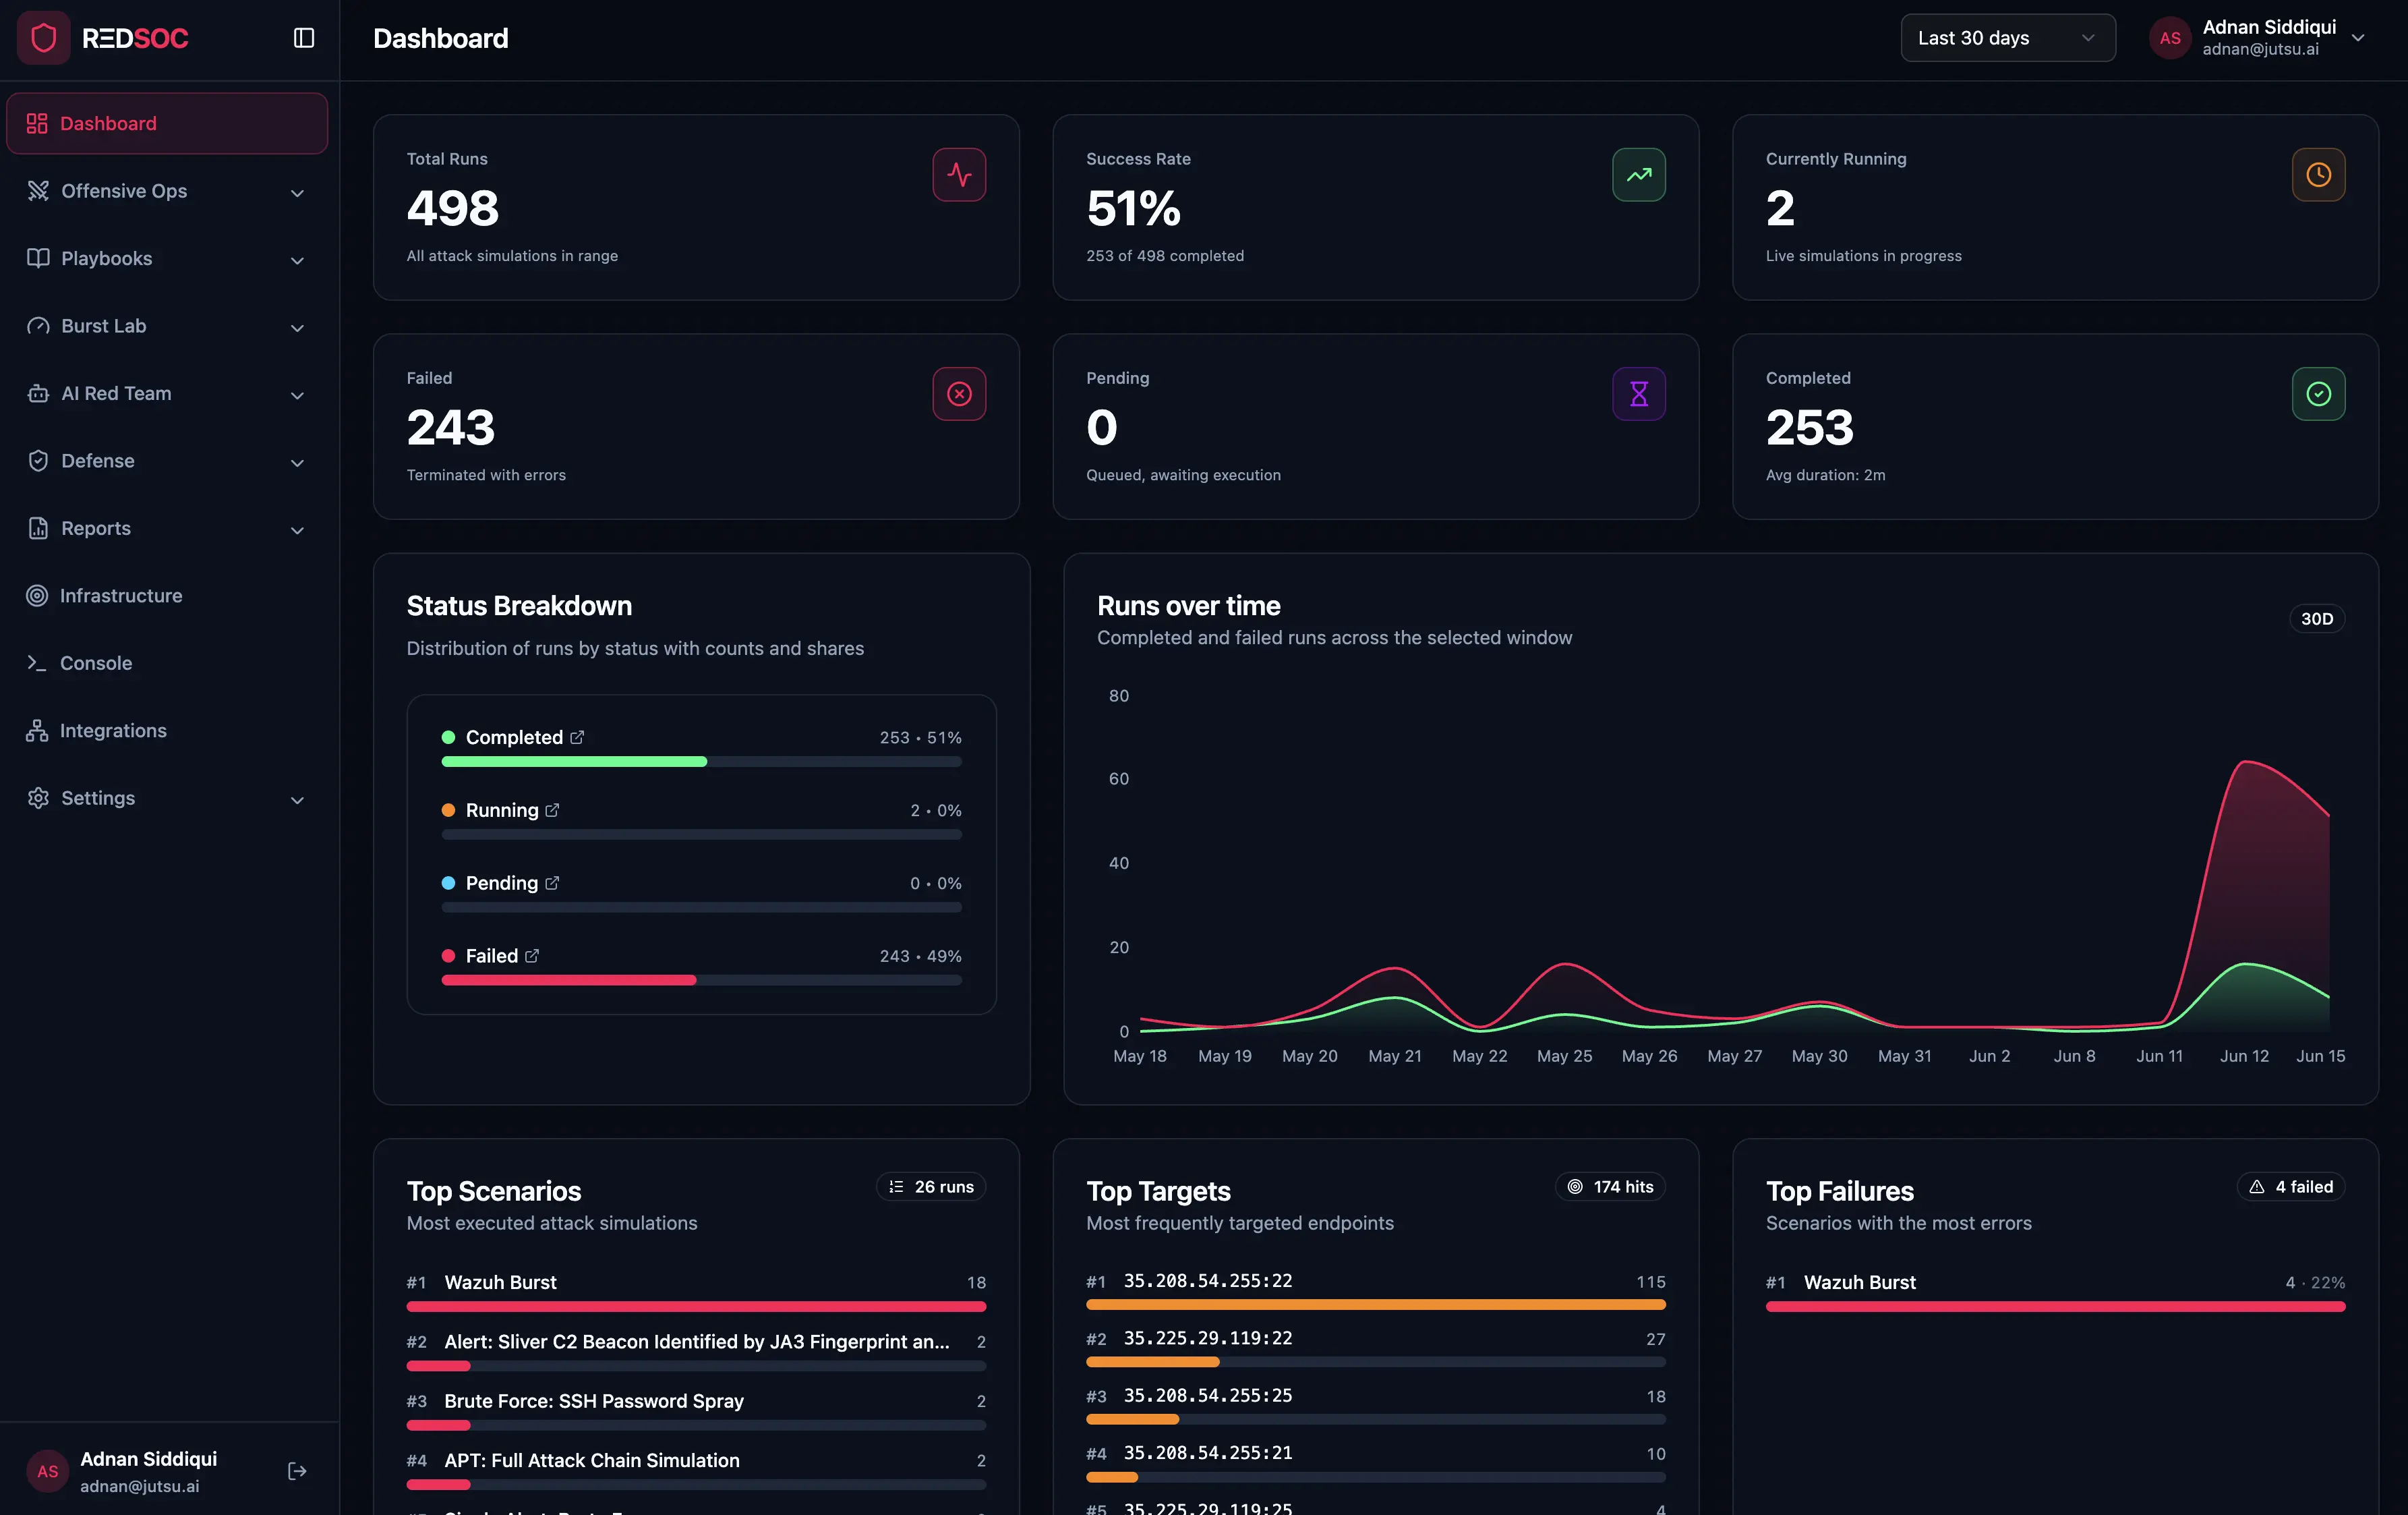
Red Team
Attack testingMITRE ATT&CK attack simulations that prove your detections work.
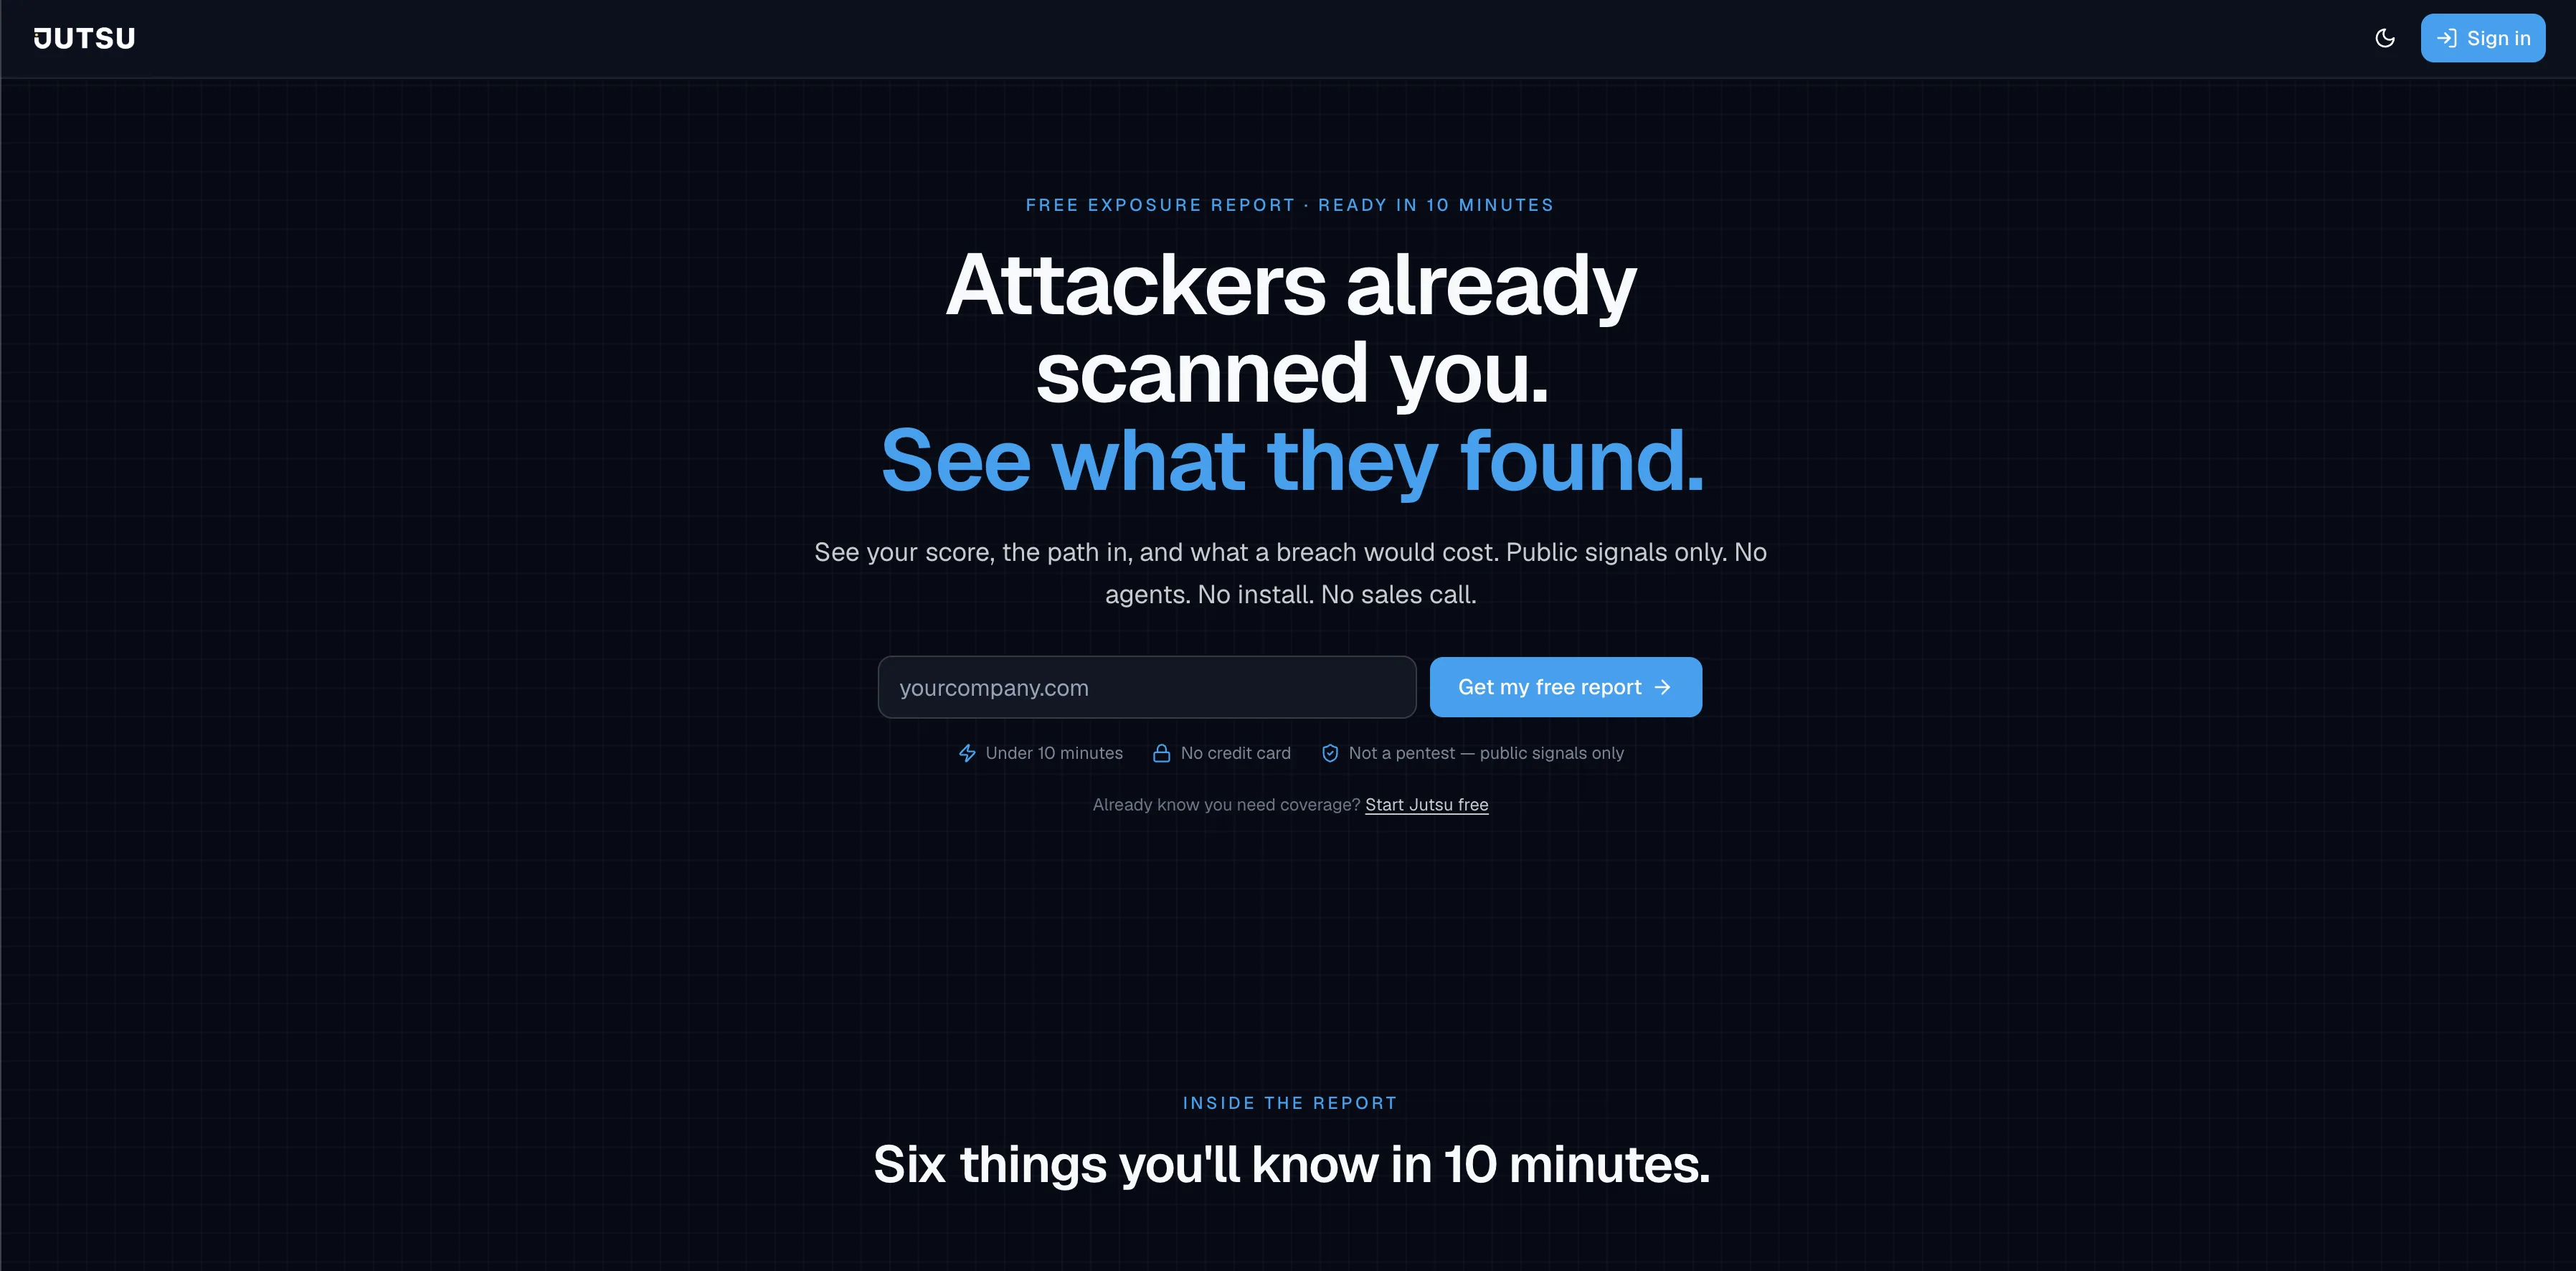
Exposure
What attackers can seeSee what attackers see, an external security assessment in minutes.
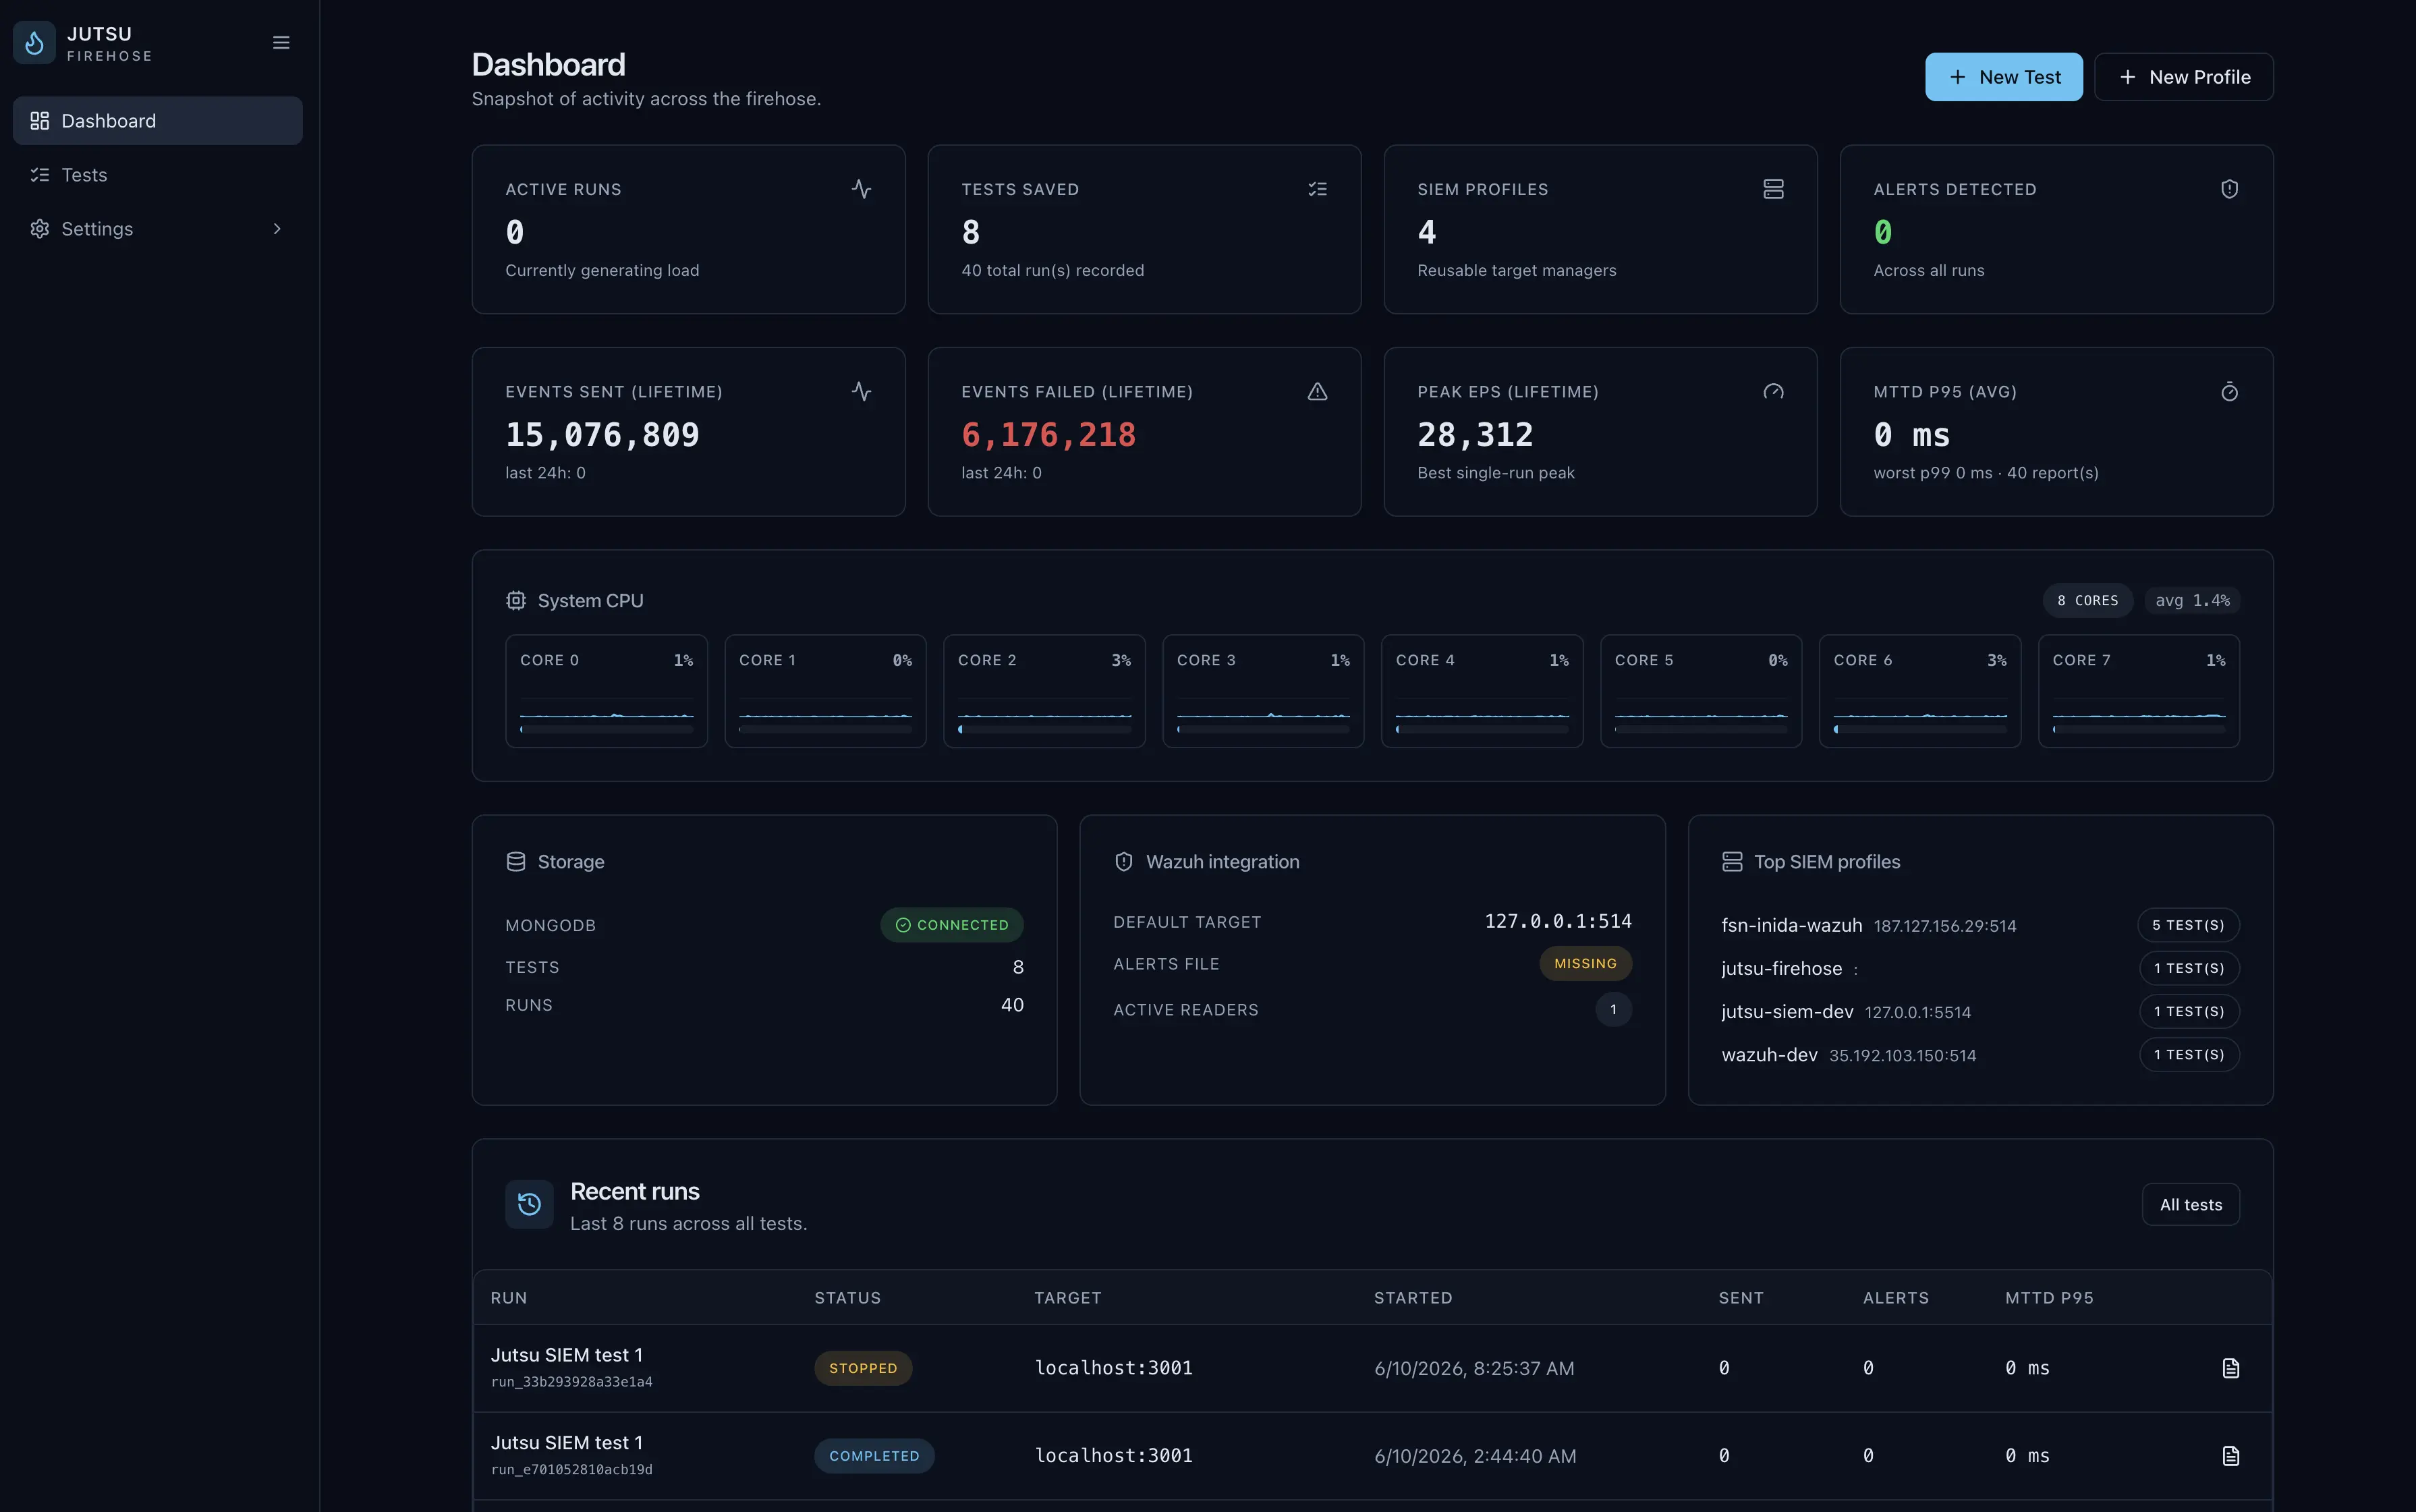
Firehose
SIEM load testingFloods your SIEM with realistic attack traffic to see if it keeps up.
Further reading
Common questions about Jutsu
Do we have to replace our existing tools?
No. AgentSOC ingests logs, alerts, and telemetry from your current stack — there's no rip-and-replace.
Do the AI agents act on their own?
On a confirmed threat, agents run the matching response playbook automatically; uncertain alerts are escalated to a human analyst, and every action is logged and reversible.
How quickly can we get started?
Connect your existing sources and agents begin triaging immediately — no lengthy deployment project.
Does it integrate with our SIEM and ticketing?
It ingests from Wazuh, Google Workspace, and syslog today, with a natural-language Copilot across your data. More SIEM and ticketing connectors are on the roadmap.
Is Jutsu self-hosted or SaaS?
The core platform is self-hosted and containerized — it runs via Docker Compose or Kubernetes, and your data stays in your own PostgreSQL, OpenSearch, and S3.
Security monitoring that runs while you build
See how Jutsu watches your systems, checks every alert, and acts only within the rules your team sets.
Subscribe to our newsletter
Get the latest security tips, product updates, and news delivered to your inbox.